Information security UAE - Locked high-security server cage inside a datacenter, steel mesh throwing lattice shadows across the floor

Home / Services / Information Security · 02 / SEC

Information Security & Risk Management

Information security and risk management for organisations across the UAE — proactive threat defence, strategic risk mitigation and a state of continuous compliance, delivered by certified ethical hackers and risk consultants, and extended to the physical premises your systems sit in.

White / Black hatFull-knowledge and zero-knowledge testing
GDPR · HIPAAISO 31000 risk frameworks
SOC + SIEMSecurity tooling advisory
Cyber + PhysicalOne layered defence strategy

What's included

Three layers, one defence posture


01 — Offensive testing

Information security, VAPT & ethical hacking

Our core competency is in proactive threat defense. We deliver advanced penetration testing and cybersecurity consulting through certified White Hat (full-knowledge) and Black Hat (zero-knowledge) experts.

We conduct rigorous Vulnerability Assessments and Penetration Testing (VAPT) on networks, endpoints, applications, and APIs, and consult on the deployment of essential security tools like SOC (Security Operations Center) tools and SIEM (Security Information and Event Management) systems.
  • Network VAPT
  • Endpoint testing
  • Application & API testing
  • White hat
  • Black hat
  • SOC / SIEM advisory
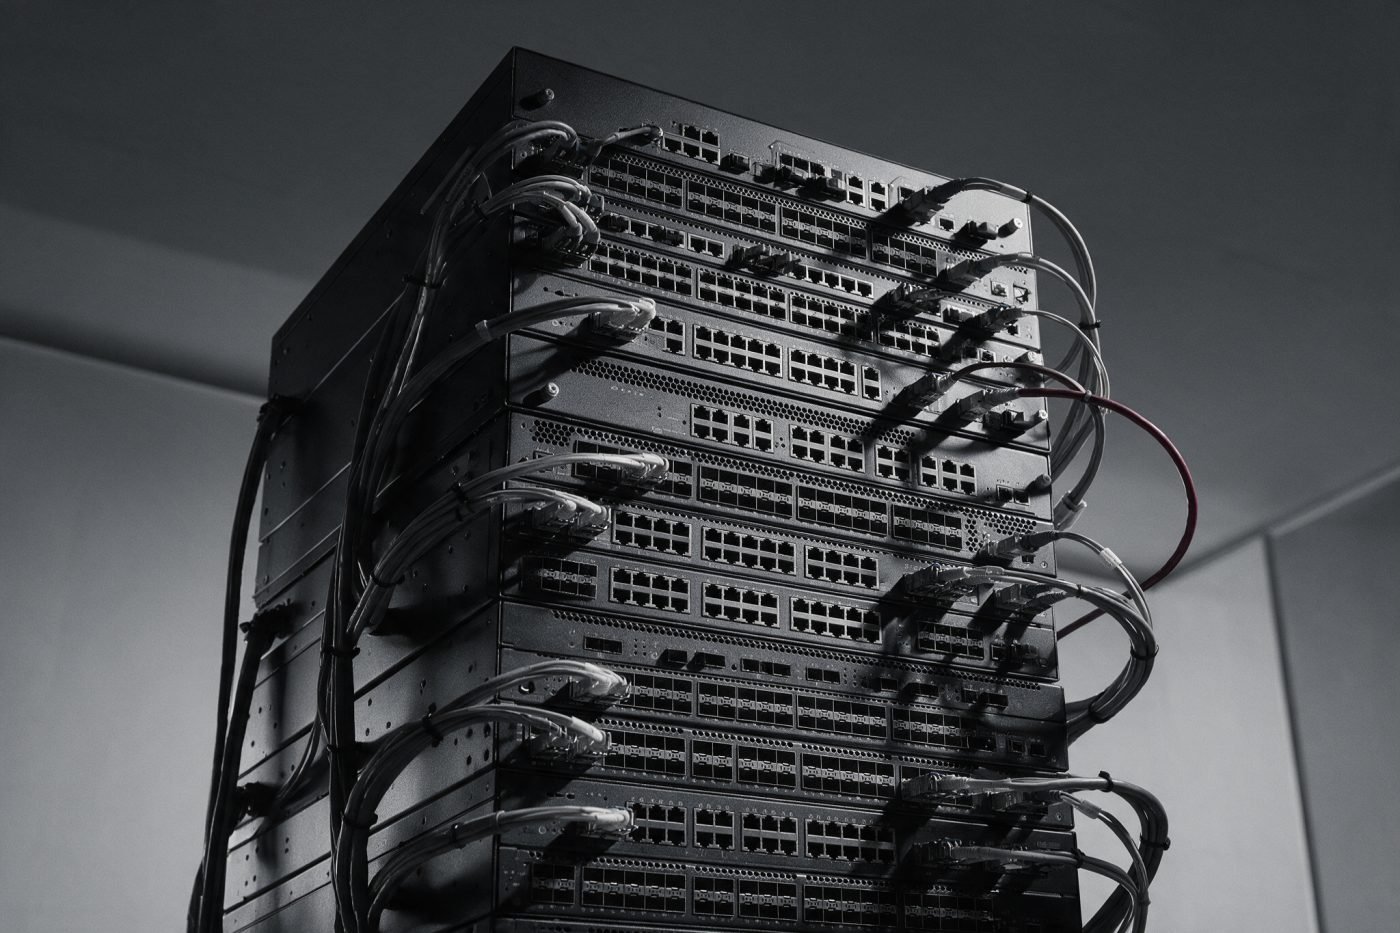
Rack-mounted firewall and network security appliance stack with dressed cabling
Security appliance stack — the perimeter under test
02 — Governance & risk

Cyber & data risk management consulting

We move beyond technical defense to high-level strategic risk mitigation. We identify, quantify, and mitigate complex cyber risks by establishing governance frameworks aligned with standards like GDPR, HIPAA, and ISO 31000.

Services include data classification, breach simulations, maintaining risk registers, and building resilient enterprise risk models that transform potential liability into a manageable business factor.
  • Data classification
  • Breach simulation
  • Risk registers
  • Governance frameworks
  • Incident response
  • Compliance reporting
Empty security operations centre facing a dark video wall
Security operations — monitoring, response and reporting
03 — Physical controls

Physical security consulting

We design and implement complete, layered defense strategies for your physical premises. This involves planning and deploying advanced CCTV and surveillance systems, biometric access control, intrusion detection, and developing comprehensive emergency planning.

Furthermore, we consult on effective facility security layouts and optimal security guard strategy and protocols.
  • CCTV & surveillance
  • Biometric access
  • Intrusion detection
  • Emergency planning
  • Facility layouts
  • Guard protocols
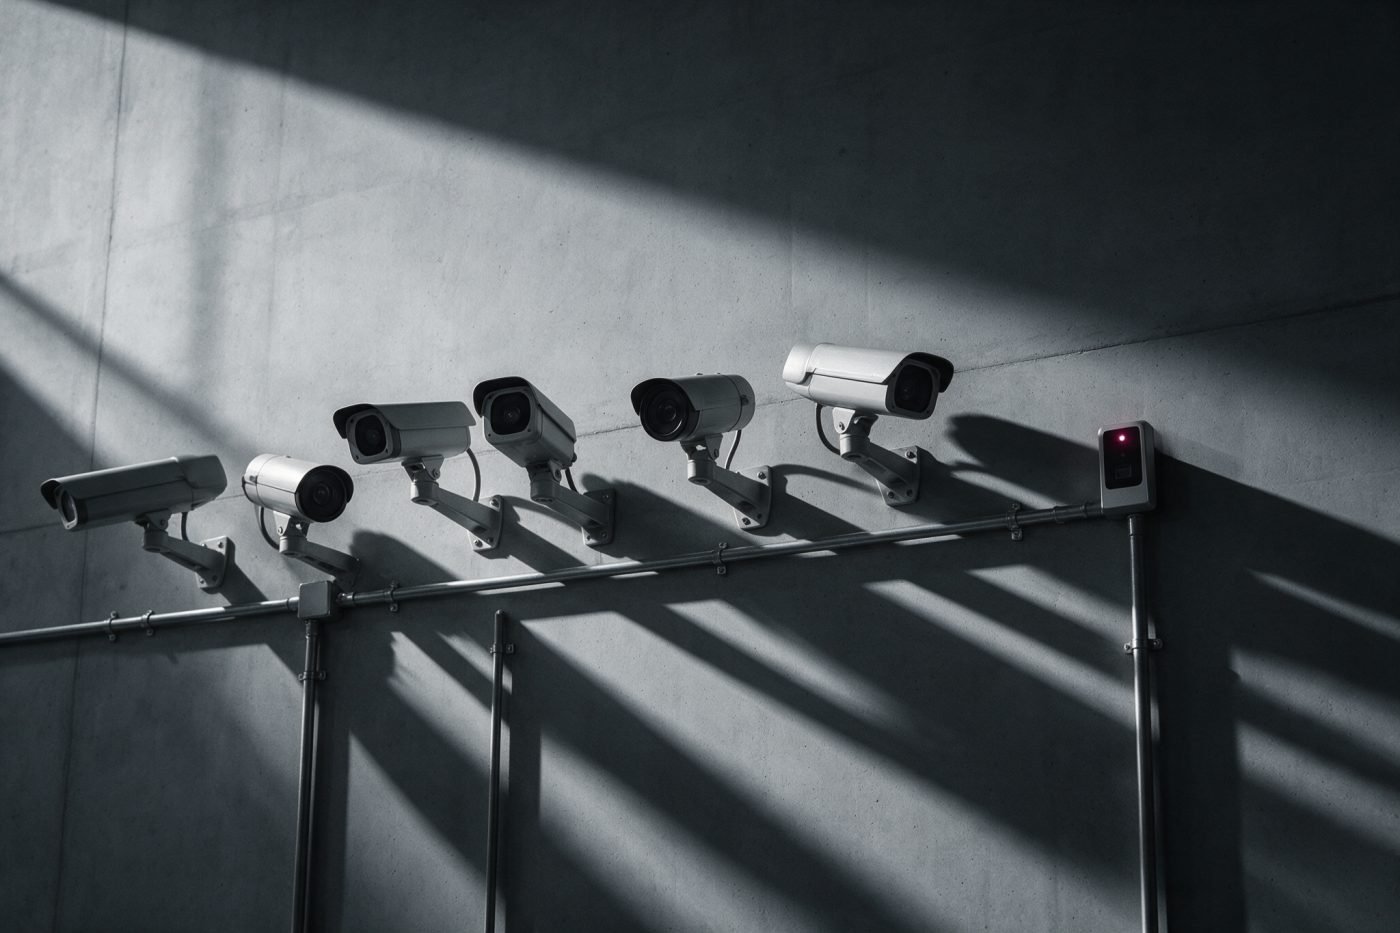
Array of surveillance cameras and a biometric access reader mounted on a concrete wall
Access control and surveillance — the premises layer

What a security engagement actually covers — each item is a deliverable, not a line in a report.

  1. Vulnerability assessment

    Networks, endpoints, applications and APIs, scoped to your environment.

  2. Penetration testing

    White hat and black hat simulation of real-world, exploitable attack paths.

  3. Risk quantification

    Cyber and data risks identified, quantified and entered into a maintained register.

  4. Governance frameworks

    Policies aligned to GDPR, HIPAA and ISO 31000, with incident response plans.

  5. Security tooling

    SOC and SIEM deployment advisory, sized to what you can actually operate.

  6. Physical controls

    Access control, surveillance, intrusion detection and facility layout consulting.

Frequently asked

Information security
questions


What is the difference between your VAPT and standard security auditing?
Our VAPT goes beyond standard auditing by conducting White Hat (known) and Black Hat (zero-knowledge) penetration testing. This simulation identifies real-world, exploitable vulnerabilities in your networks and applications, providing a deeper defense posture than simple compliance checks.
How does your Cyber Risk Management service address data privacy?
We develop enterprise frameworks to identify, quantify, and mitigate risks aligned with global standards like GDPR and HIPAA. Our service focuses on data classification, governance, and establishing robust incident response plans to ensure compliance and minimize liability.
Do you only focus on cyber threats, or physical security too?
Our approach is holistic. We integrate cyber defenses with physical security controls, advising on access control systems, surveillance, and facility layouts. We ensure your premise security is as robust as your network security.
Locked high-security server cage inside a datacenter

Find the gaps before someone else does

Tell us the challenge. We'll tell you what it actually takes — scope, expertise and timeline — before anyone signs anything.
Scroll to Top